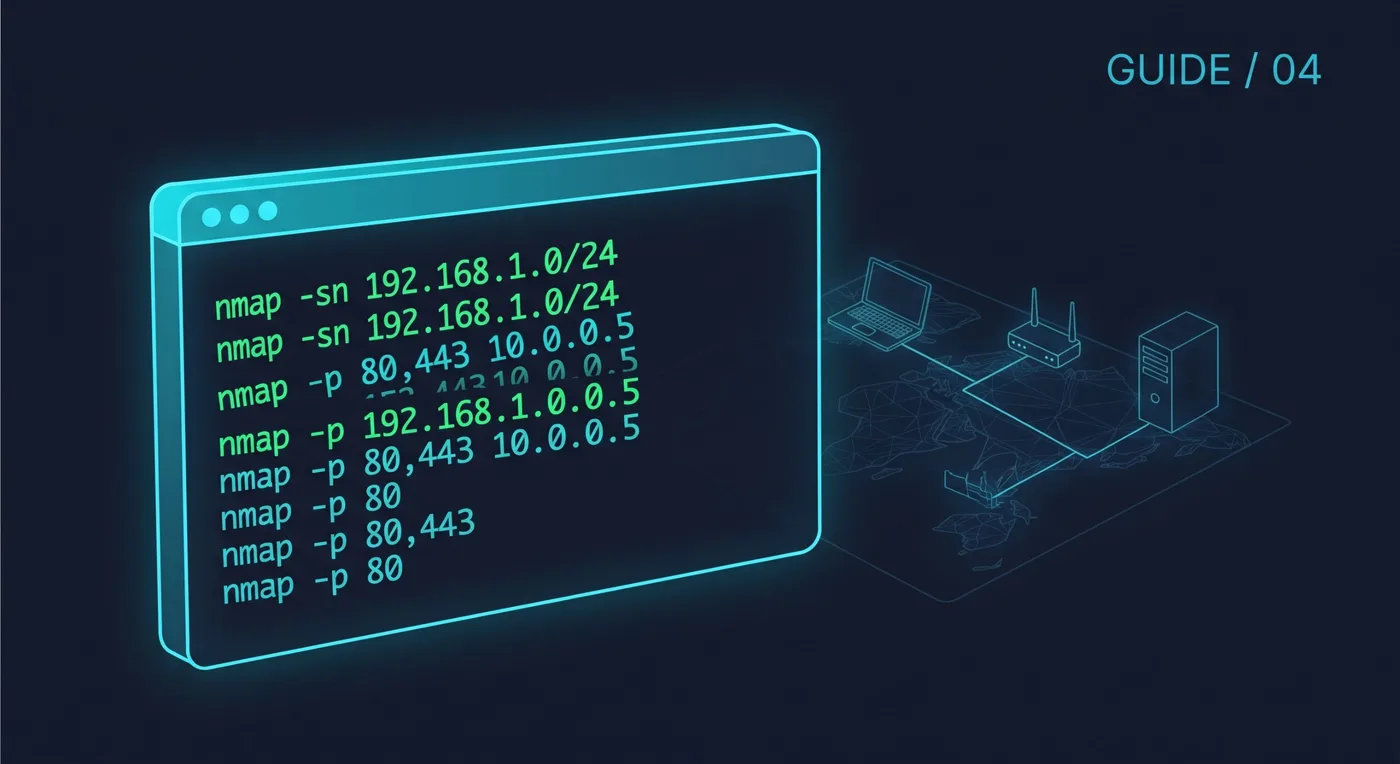
Nmap is the standard tool for finding out what is running on a network. Before anything else: only scan machines you own or have written permission to test. A home lab or a few virtual machines is the right place to practise.
1. Find live hosts
nmap -sn 192.168.56.0/24-sn skips the port scan and only checks which hosts respond. It is a quick map of your lab.
2. Scan the common ports
nmap 192.168.56.10By default Nmap checks the 1000 most common TCP ports and reports each as open, closed or filtered. Filtered usually means a firewall is dropping the probe.
3. Detect services and versions
nmap -sV -p 22,80,443 192.168.56.10-sV asks each open port what is listening, for example OpenSSH or Apache, and which version. Old versions are the first thing to patch.
4. Scan every port and save the result
nmap -p- -oN scan.txt 192.168.56.10-p- covers all 65535 ports, and -oN writes a readable report you can compare after hardening the server.
A simple lab exercise
- Scan a fresh Linux VM and note the open ports.
- Harden it: remove unused services and add firewall rules.
- Scan again and check that only the ports you intended are still open.
Keep your scan files. Comparing a before and after scan is the easiest way to prove a hardening step worked.